26 Oct 26
A meeting invitation arrives while you are getting ready for the next call. The branding looks familiar, the subject sounds routine, and the join button asks you to sign in. Would your team treat that invitation with the same care as an unexpected email?
On 15 October 2026, Check Point Email Researchers reported campaigns using fake calendar invitations to steal Microsoft account credentials. Some used valid calendar attachments; others used misleading meeting links. The researchers described an increase beginning on 25 September. This was abuse of familiar calendar features and trust, rather than evidence that every invitation exploits a software vulnerability.
For Australian business leaders, the useful question is whether your everyday meeting workflow is included in your phishing controls. You do not need to wait for an incident to find out.
A calendar entry can feel like an instruction to attend rather than a message to assess. That matters for reception teams, executive assistants, sales staff and anyone regularly meeting customers or suppliers. An unfamiliar organiser is sometimes entirely legitimate, so a blanket rule to reject external meetings would create its own operational problems.
Consider this illustrative example: an employee receives an unexpected supplier review invitation and follows a sign-in link before checking with the account owner. The business needs more than a reminder to be careful. It needs a simple way to verify the meeting, a reporting route the employee can find quickly, and an IT response that considers the account as well as the invitation.
The Australian Signals Directorate’s guidance on socially engineered messages recommends pausing before acting on unexpected requests, confirming them through a trusted method and reporting suspicious messages through the organisation’s security process.
Apply that principle to meetings: if the request is unexpected or the sign-in step seems unusual, contact the organiser using an existing contact record or another independently verified channel. Do not use a phone number supplied only inside the suspicious invitation. A familiar logo or polished wording should not settle the question.
Make the reporting instruction specific to your workplace. Tell staff which approved reporting button or helpdesk channel to use, and what to do if they cannot access email. Avoid asking them to circulate a live suspicious invitation to colleagues to see whether anyone else received it.
Request a controlled review using harmless test content and designated test accounts. Include the desktop and mobile calendar clients your people actually use, plus any shared or delegated calendars. Agree the test scope before sending anything, and avoid real malicious links or simulated credential collection.
The review should answer four operational questions:
Record the observed results rather than assuming all clients behave identically. Ask IT to check the controls and remediation features available in your actual environment, including licensing and configuration. A product name on an invoice is not evidence that a particular workflow has been tested.
Review any proposed restriction with the people who depend on external meetings. Reception may book appointments for several staff; an assistant may manage an executive’s diary; a project team may receive invitations from new suppliers every week. These are different working patterns.
Pilot changes with a small representative group. Check whether genuine invitations arrive, updates reach attendees and cancellations behave as expected. Name an owner for exceptions and give temporary workarounds a review date. The aim is a process staff can follow reliably, rather than one that encourages them to bypass controls to keep working.
A useful reporting process welcomes early disclosure, including “I entered my password” or “I approved a prompt”. Staff should stop interacting with the suspicious content and contact the approved support channel immediately, explaining what happened and when. They should not be expected to investigate a potentially malicious site themselves.
Ask the IT or security team to assess whether account containment, session review, credential changes or further investigation are needed. Removing an invitation alone does not establish that an account is safe. The appropriate response depends on what the person did and the evidence available; avoid a one-size-fits-all instruction to delete everything before it can be examined.
Bring your operations lead and IT contact together for a short review. Choose one common external-meeting workflow and document who verifies unusual requests, where staff report concerns, who investigates and how completion is confirmed. Give any gap an owner and a due date.
At Zarbtech, our view is that security controls are most useful when they fit the way your business operates. Our cybersecurity services include employee awareness and technical protection, while our Managed IT services provide day-to-day support and practical guidance. Bring your meeting and reporting workflow to a conversation about the support and improvements your organisation needs.
22 Oct 26
A fast AI answer is only part of the job. Compare accepted results, checking time and costs before…
20 Oct 26
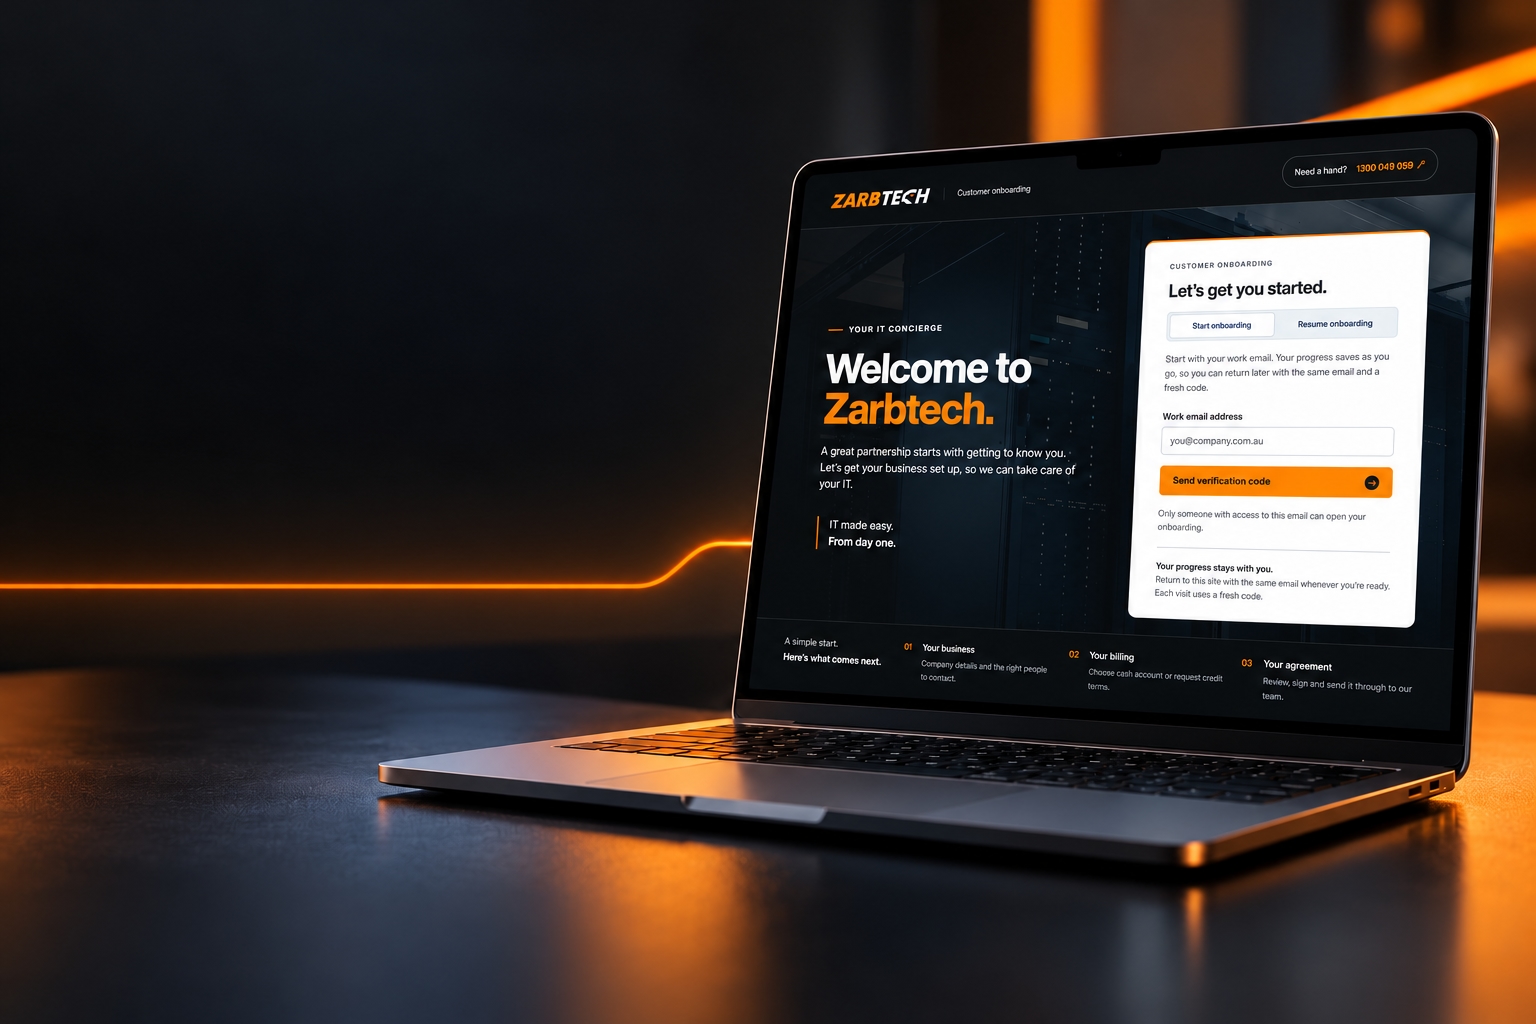
A simpler start to working with Zarbtech: our new onboarding website brings business details, billing preferences and your…